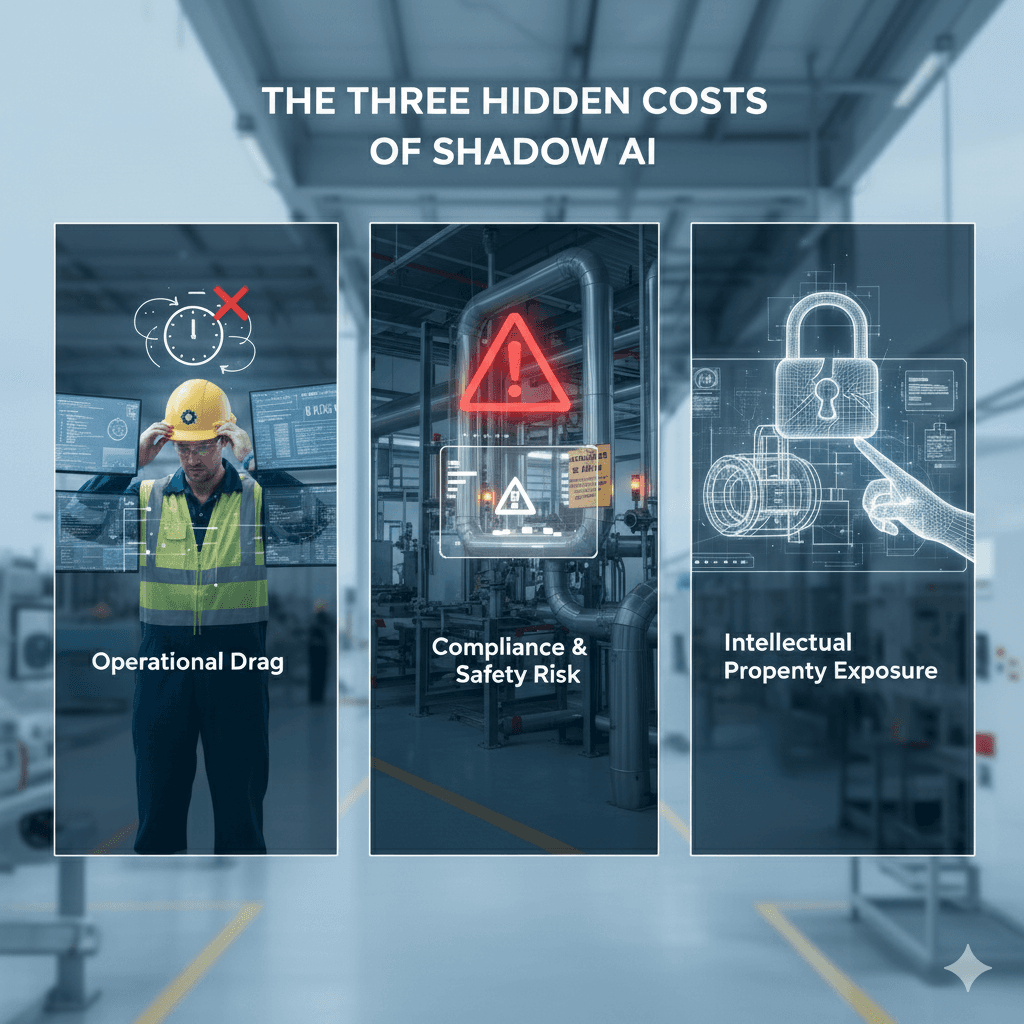
Shadow AI is the use of AI tools, accounts or connections outside an organisation's approved process. In industrial operations, it may include staff pasting maintenance notes into a public chatbot, uploading a manual to an unapproved account or using AI to draft a safety document without a defined reviewer.
The practical response has three steps: discover the work people are trying to complete, set rules they can follow and provide an approved workflow that solves the same problem.
Why Does Shadow AI Appear in Industrial Operations?
People usually adopt unapproved tools because the work is slow and the available process doesn't help. A maintenance coordinator needs to find a procedure. A project manager has several pages of site notes to turn into a report. An engineer wants to compare technical documents.
That initiative is useful evidence. It shows where the team sees value. The risk comes from uncertainty about the information entered, provider terms, permissions, output quality and human review.
Treat shadow AI as a process and leadership issue, not only a disciplinary problem. If the organisation removes a tool without addressing the work, the same demand will appear elsewhere.
What Risks Need to Be Assessed?
Don't assume every use creates the same exposure. Record the actual task and assess:
- Information: Does it include personal information, commercial terms, equipment data, drawings, procedures or incident records?
- Provider access: Can the provider retain, review or use prompts, files and outputs under the account's terms and settings?
- Output consequence: Is the system drafting a low-consequence summary or influencing safety, quality, employment or financial decisions?
- Permissions: Can the tool only read information or can it write to business systems?
- Review: Who checks the output, against which source and before what action?
- Traceability: Can the business reconstruct what information and instruction produced the result?
In New Zealand, the Privacy Commissioner says the Privacy Act applies to agencies using AI. In Australia, the OAIC recommends due diligence, human oversight and ongoing review where personal information is involved.
Safe Work Australia also advises organisations to manage work health and safety risks from AI and digital technologies through their existing risk processes. An AI policy doesn't replace the site's safety, quality, privacy or change-control responsibilities.
Step 1: Discover the Work and Current Use
Start with a short, non-punitive discovery process. People are more likely to disclose useful examples when the goal is to improve the work rather than catch them breaking a rule.
For each use, record:
- The task and how often it occurs.
- The tool, account type and connection used.
- The information entered or accessed.
- The output and what happened next.
- The time saved or rework created.
- The person who checked the result.
- The consequence if it was wrong.
Combine interviews with the technical evidence you are authorised to review, such as approved-app inventories, expense data, browser controls or system logs. Follow your employment, privacy and security obligations when collecting that evidence.
The output should be a prioritised register, not a catalogue of every experiment. Separate low-consequence personal productivity from shared workflows and consequential use.
Step 2: Set Practical Rules and Controls
Write rules around information and actions, not a list of brand names that will become stale.
The policy should state:
- which tools and account types are approved
- which information must not enter public or unapproved tools
- which uses require privacy, security, safety or legal review
- when source references and human approval are mandatory
- which systems an AI tool may read from or write to
- how staff report an error, incident or useful new use case
Keep the first version short enough to use. Add role-specific guidance where the consequence differs, such as maintenance, health and safety, finance or people operations.
A policy needs an owner and an update rhythm. It also needs an approved alternative. Otherwise, staff face the same operational pressure with fewer visible options.
Step 3: Move Useful Demand Into Approved Workflows
Choose one recurring use from the discovery register. Define the approved source information, permissions, test cases, reviewer and baseline before selecting the technology.
For example, a procedure-retrieval capability may return the relevant passage from the current approved document and show its source. The operator still checks the source and applies the authorised procedure. The system doesn't invent or approve a safety instruction.
An inspection-document workflow may extract fields into a review queue and flag missing information. A qualified person remains responsible for the record and the operational decision.
Test representative and difficult cases. Keep a record of corrections and rejected outputs. Release the capability to a small group, then compare the result with the current workflow before expanding it.
How Do You Measure Progress?
Use operating and control measures together:
| Measure | Example |
|---|---|
| Unapproved use | Number and type of active uses found through the agreed review process |
| Approved adoption | Target users completing the workflow in the approved environment |
| Output quality | Accepted, corrected and rejected outputs against defined test cases |
| Workflow result | Retrieval time, processing time, rework or completeness against baseline |
| Control performance | Exceptions, policy questions, incidents and review completion |
| Source health | Current, superseded and ownerless documents in the approved set |
Our hidden-cost framework explains how to calculate observed correction and review time without treating potential capacity as cash. The manufacturing AI guide covers operational starting points and safety controls in more detail.
If you want to turn one shadow AI use into a controlled workflow, tell us about your business.